Your data.
Visible. Accessible.
Under control.
One continuous system, not a one-time scan.
Know what exists. Know who can reach it.
Select a data asset — the catalogue and the identities that can reach it update together.
Your enterprise, mapped as a living system.
Systems, data, identities and the policy that governs them — one connected map of relationships, access and risk, not a static inventory.
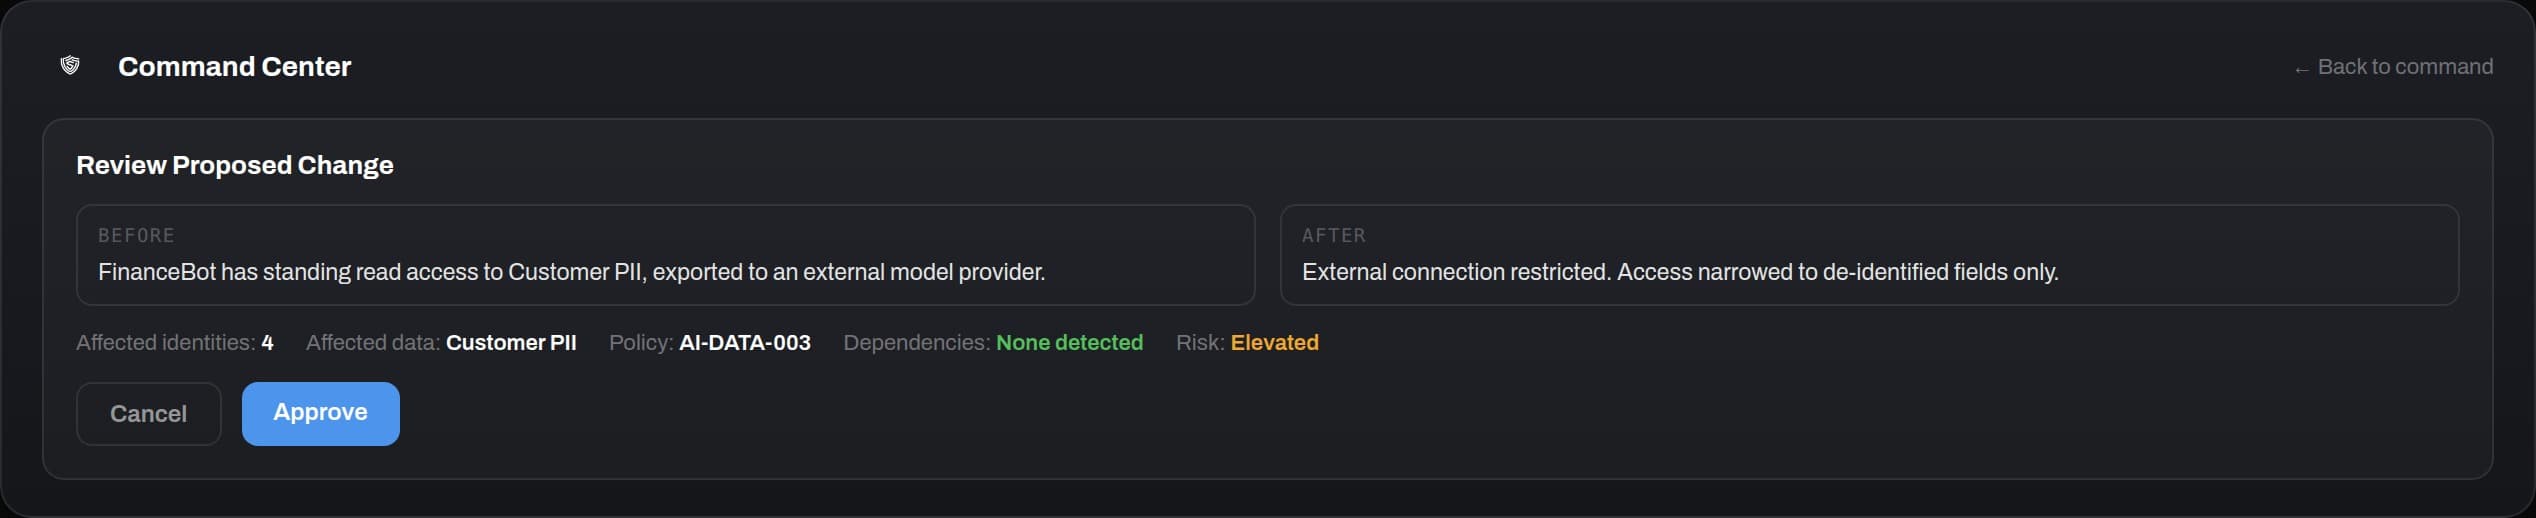
Governs Customer PII and flags export to External Model Provider as a policy violation.
Turn policy into infrastructure.
Policies evaluate enterprise data activity and determine the outcome:
Enforcement depends on the integration in place for a given system — where a policy can only be monitored, Sentinel says so rather than implying universal blocking.
Governance posture and control coverage — not a legal compliance certification.
Ask Sentinel anything about your data estate.
One continuous investigation into Sentinel's own governed metadata and Data Graph — not a general chatbot. Click through a real example, end to end.
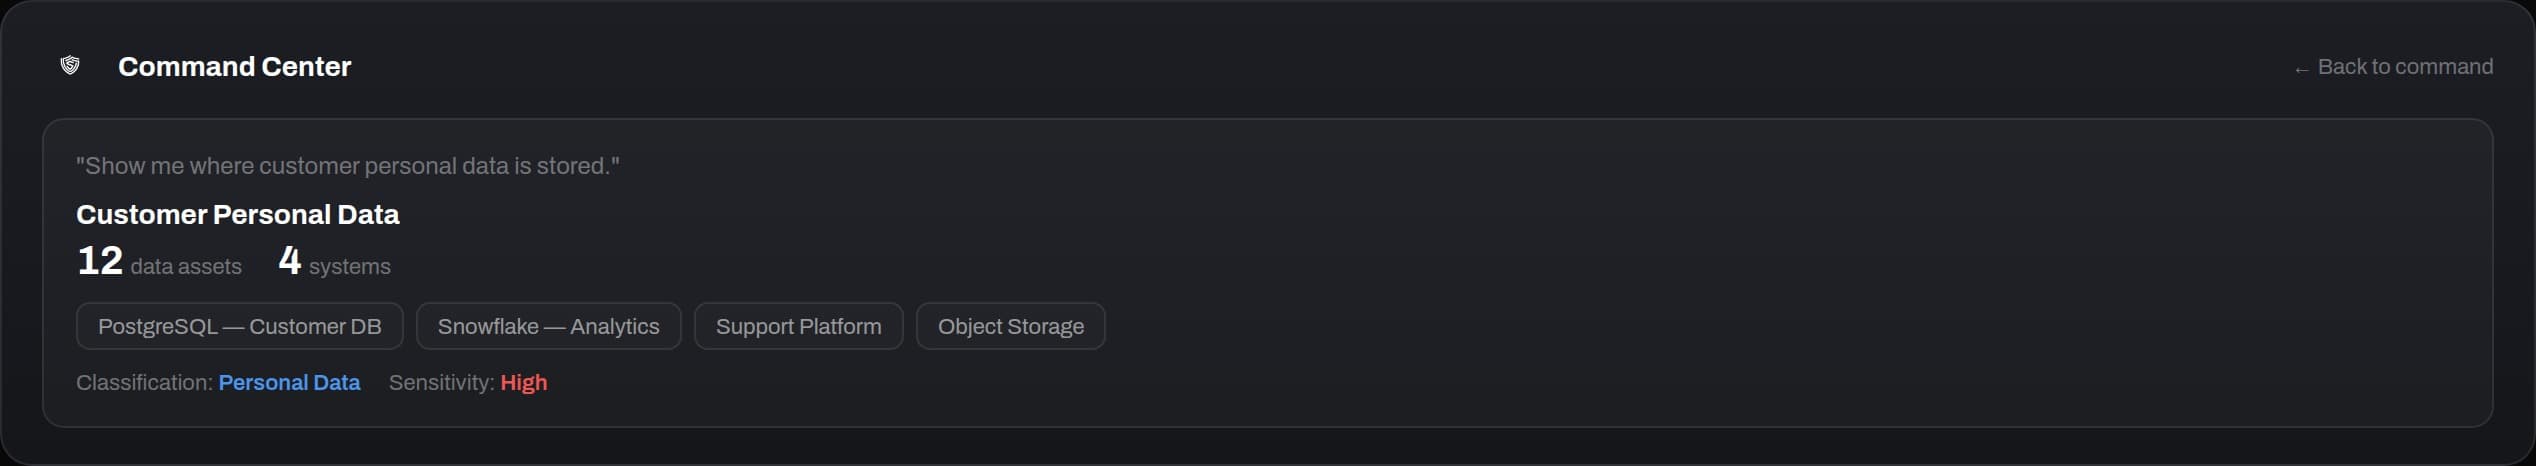
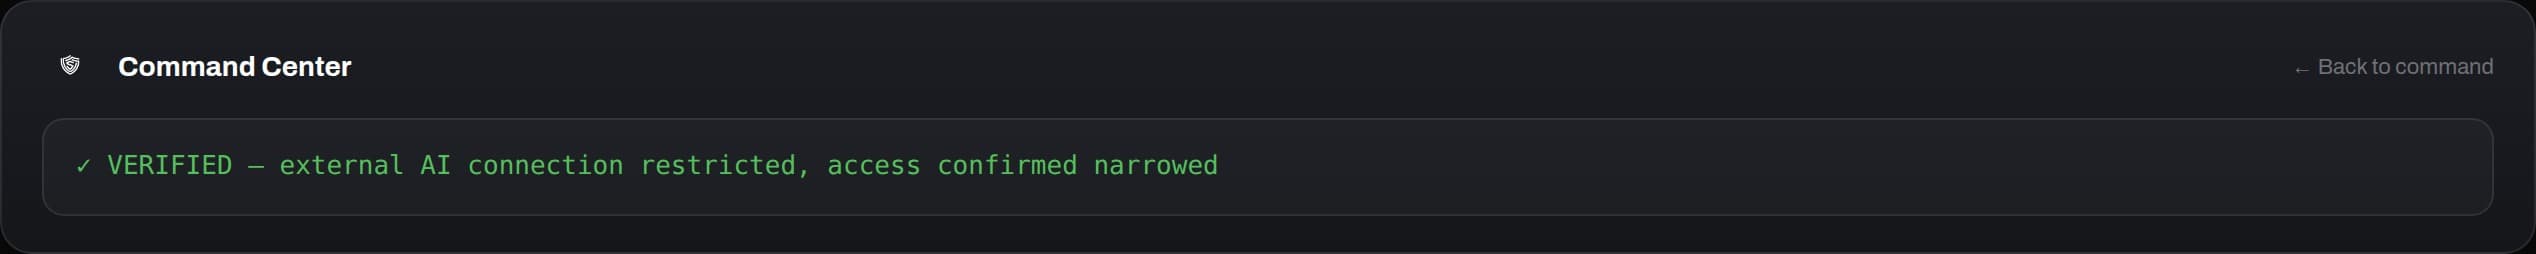
From violation to verified remediation.
Sentinel does not execute sensitive actions on its own. It proposes a governed change, a human reviews and approves it, and every step is recorded.
Connects securely to your environment.
Sentinel connects through secure connectors — it does not copy an organisation's raw data into Porthos infrastructure.
Illustrative scenarios, one industry at a time.
Financial Services
See which systems, applications and AI agents can access sensitive financial and customer data, enforce access policies, and maintain an auditable record of what happens to it.